
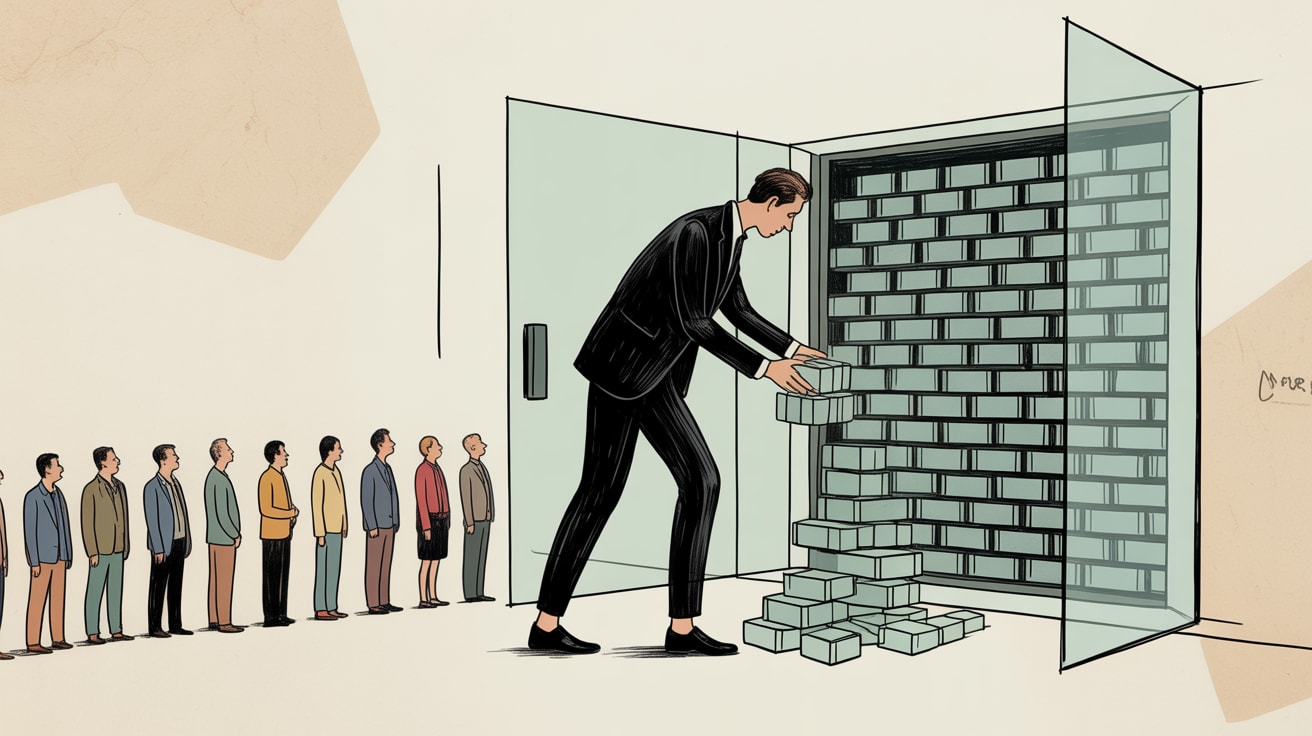
Australia's 2026 privacy overhaul goes far beyond consent banners. Here's what Southeast Asian data teams must do now to turn compliance into competitive edge.
Consent banners have always been a fiction. They create the appearance of control while burying the actual data contract in 4,000 words of legal prose that nobody reads. Australia’s 2026 privacy exposure draft is calling time on that arrangement — and for brands operating across Southeast Asia with any Australian customer exposure, the implications run much deeper than your cookie settings.
What Australia’s 2026 Exposure Draft Actually Changes
The Attorney-General’s Department’s exposure draft represents the most significant overhaul of Australia’s Privacy Act in over a decade, according to Tealium’s analysis of the legislation. The changes that matter most to customer data teams aren’t the headline consent requirements — they’re the operational ones buried underneath.
Specifically: the draft introduces a strengthened definition of personal information that brings inferred and derived data explicitly into scope. If your data science team is building behavioural segments from clickstream data, those segments may now carry the same compliance obligations as the raw identifiers that generated them. That’s a material shift. It means your data activation layer — the place where clean data becomes targeting criteria — needs its own governance logic, not just a consent flag inherited from collection.
For teams running customer data platforms across APAC, this creates immediate audit pressure. The question is no longer “did we collect this with consent?” but “does our use of this data fall within what the customer reasonably expected when they gave it?”
The Architecture Problem Nobody Wants to Talk About
Most brands’ first-party data programmes were built to solve a measurement problem, not a trust problem. They were assembled in response to third-party cookie deprecation, with the primary design goal of keeping attribution models intact. Consent was bolted on — often literally, via a tag manager rule that fires a consent string to ad platforms before anything else happens.
That architecture is now a liability. When regulations like Australia’s reform ask you to demonstrate that data use aligns with original consent intent, a consent string attached to a tag isn’t an answer. It’s a starting point for an uncomfortable conversation with your legal team.
The more durable approach — one that Smart Communications’ record growth in regulated industries quietly validates — is building communications infrastructure where consent state is a first-class data attribute, not an afterthought. Smart Communications reported record bookings growth driven by demand in regulated sectors, precisely because compliance-forward design is becoming a procurement criterion, not just a regulatory checkbox. Brands that can demonstrate consent architecture to enterprise buyers are closing deals that their less-prepared competitors are losing.
What Southeast Asian Teams Should Be Doing Right Now
Australia’s reform isn’t Southeast Asia’s law. But three things make it directly relevant to teams in this region.
First, many brands operating across APAC hold Australian customer data and will be in scope regardless of where their headquarters sit. Thailand’s PDPA, Singapore’s PDPA amendments, and Indonesia’s PDP Law are all tightening in similar directions — Australia is simply the most detailed signal of where the region is heading.
Second, mobile-first data collection in Southeast Asia creates specific exposure. In markets where the dominant consumer touchpoint is a super-app or a marketplace platform like Shopee or Lazada, brands often collect rich behavioural data through platform integrations that sit outside their direct consent flows. When regulators start asking about inferred data — as Australia’s draft does — that platform-collected data becomes a grey area that needs active management, not hopeful ambiguity.
Third, multilingual consent interfaces are genuinely hard to get right. A consent experience that reads as clear and unambiguous in English may carry different implications when rendered in Bahasa Indonesia or Thai. Teams implementing consent management platforms across Southeast Asian markets should be conducting language-specific user testing on consent flows, not just translation reviews. The legal standard is informed consent; the practical standard is whether a real user in that market actually understood what they agreed to.
Turning Compliance Pressure Into a Data Asset
The brands that will emerge from this regulatory cycle in the strongest position are the ones treating it as an opportunity to rebuild data trust from the ground up — not the ones minimising compliance surface area.
Practically, that means three things. One: conduct a data use audit that maps every activation use case back to its consent basis, and identify gaps where data use has drifted beyond original intent. Two: invest in preference centres that give customers genuine control, with granular options rather than binary opt-in/opt-out — this is both better practice and better data, because customers who choose their preferences are more engaged with the resulting communications. Three: build consent state into your data model as a persistent, queryable attribute so that when regulators or enterprise buyers ask for evidence of compliant data use, you can produce it in hours rather than weeks.
The brands that do this well will have something their competitors don’t: a first-party data programme that customers actively trust, regulators can audit, and enterprise partners are willing to integrate with. That’s not a compliance cost. That’s a durable competitive asset.
Key Takeaways
- Audit every data activation use case against its original consent basis — inferred and derived data are now explicitly in scope under Australia’s draft, and similar logic is coming across Southeast Asia.
- Rebuild consent as a first-class data attribute in your CDP or data warehouse, queryable and auditable, not just a flag attached to a tag.
- Treat multilingual consent interfaces as a UX problem requiring user testing, not a translation problem requiring a language review.
The uncomfortable question for most marketing teams isn’t whether their data practices are legal — it’s whether they’d survive a plain-language explanation to the customers whose data they hold. As privacy reform raises that bar across APAC, the gap between “technically compliant” and “genuinely trusted” is where competitive advantage will be built or lost. Which side of that gap is your current data architecture designed to live on?
At grzzly, we help brands across Southeast Asia build first-party data programmes that are designed for compliance from the start — not retrofitted to it. Whether you’re auditing existing consent flows, rebuilding your data architecture ahead of regional regulatory shifts, or trying to turn preference data into a real engagement asset, we’d rather work through it with you before the regulator asks the questions. Let’s talk
Sources
Written by
Lavender GrizzlyTurning privacy constraints into competitive advantage. Builds first-party data programmes that are compliant by design, valuable by intent, and trusted by the people whose data they hold.